Blog
[Advanced Spring Boot] Your Own Authorization Server: Spring Authorization Server and Keycloak
Building an OAuth2 and OpenID Connect authorization server with Spring Authorization Server, now a module of Spring Security, on Spring Boot 4.1.1: the starter Initializr picks and the deprecated one, a server from properties alone, both discovery documents and the endpoints they advertise, the two filter chains Boot registers and what changes when you declare your own, client_credentials and authorization_code with PKCE hop by hop, the real error bodies, the RSA key that changes on every restart, a persistent key and key rotation with a JWK selector, the JWKS cache of the resource server, JDBC clients, authorizations and consent on PostgreSQL with the schema scripts from the jar, a roles claim from OAuth2TokenCustomizer and the Jackson allowlist trap, opaque tokens with introspection measured against JWT validation, and a measured comparison with Keycloak.
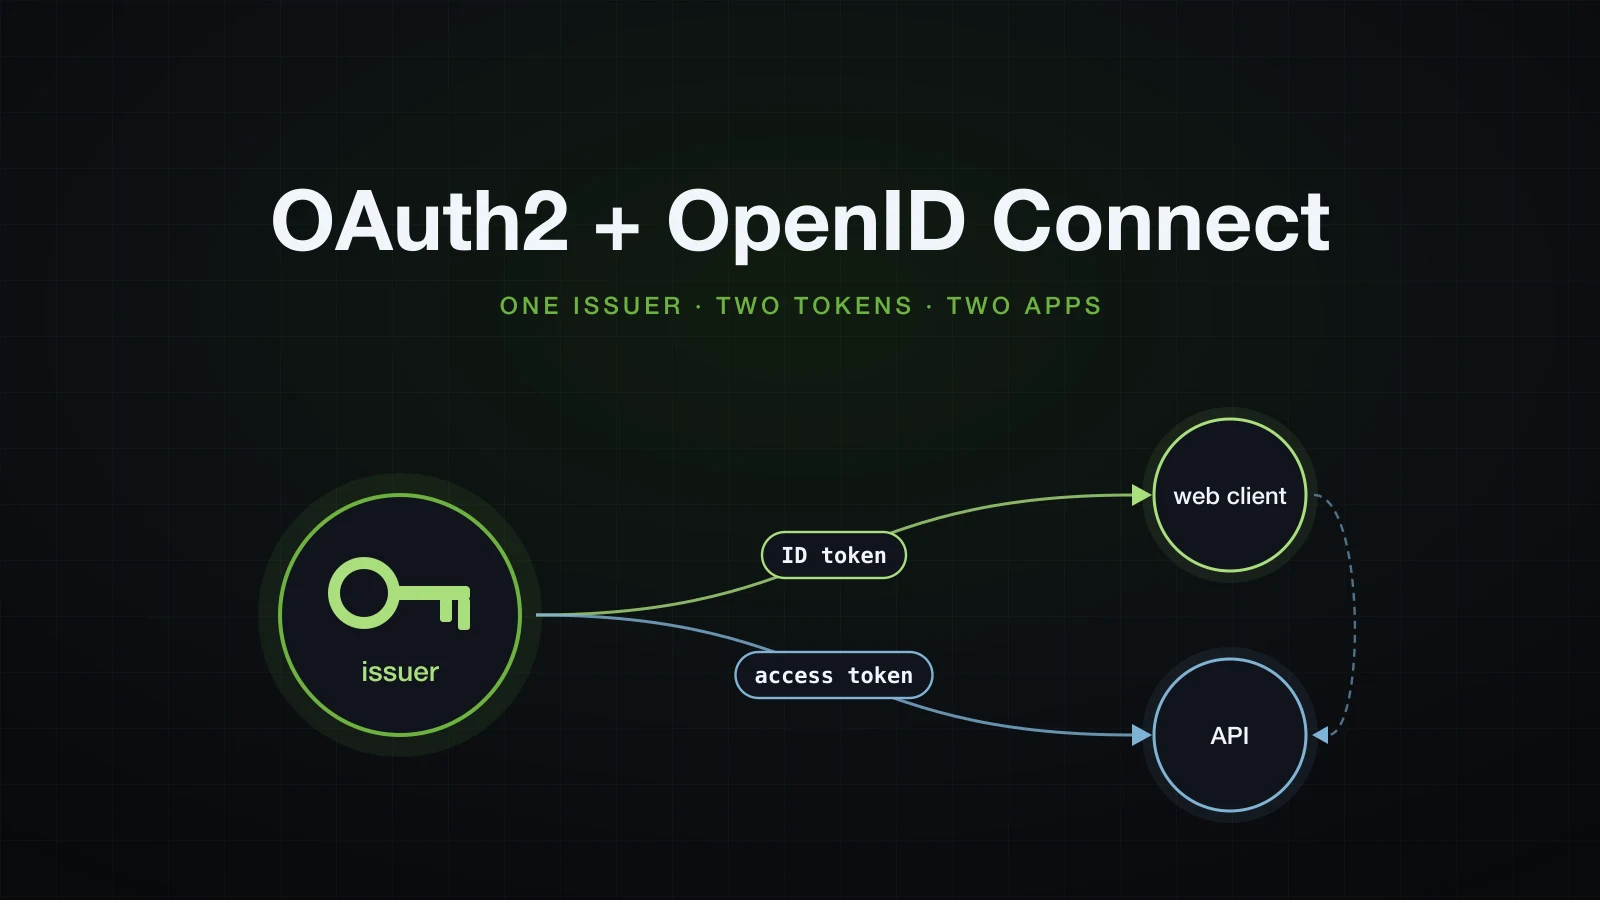
[Advanced Spring Boot] OAuth2 and OpenID Connect in Spring Boot: OAuth2 Login and a JWT Resource Server
OAuth2 and OpenID Connect with Spring Security on Spring Boot 4.1.1 and Keycloak: a realm imported from JSON, issuer-uri discovery and the startup failure when Keycloak is down, the authorization code flow with PKCE (S256, on by default for a confidential client) hop by hop, a stolen code rejected without its verifier, the ID token and the access token decoded side by side, the OidcUser with its OIDC_USER and SCOPE_ authorities, user-name-attribute, Keycloak realm roles mapped to ROLE_ with a GrantedAuthoritiesMapper, RP-initiated logout with OidcClientInitiatedLogoutSuccessHandler, Google and GitHub through CommonOAuth2Provider, a JWT resource server with issuer-uri and lazily fetched keys, the WWW-Authenticate headers for foreign-realm, wrong-issuer, tampered, wrong-audience and expired tokens, realm_access.roles mapped with authorities-claim-expressions, token relay with OAuth2ClientHttpRequestInterceptor and a client-credentials token reused across calls.
[Advanced Spring Boot] Multi-Tenancy and Soft Delete with Spring Boot and Hibernate
Multi-tenancy and soft delete on Spring Boot 4.1.1 with Hibernate and PostgreSQL: an X-Tenant-Id filter with a ThreadLocal that leaks on a reused Tomcat thread and is lost on @Async, a discriminator column with @TenantId and CurrentTenantIdentifierResolver (the tenant predicate on find, JPQL, derived queries, Specifications and bulk updates, none on native SQL or JdbcClient), schema per tenant with a MultiTenantConnectionProvider, the setSchema versus SET search_path connection-reuse trap on HikariCP, Flyway per tenant schema and Hibernate's TenantSchemaMapper, database per tenant and 100 connections for ten tenants, PostgreSQL row-level security with set_config and FORCE, @SoftDelete strategies versus @SQLDelete and @SQLRestriction, the LAZY to-one error, a partial unique index for soft-deleted SKUs, and restoring deleted rows.
[Advanced Spring Boot] NoSQL with Spring Data: MongoDB and Redis
Spring Data MongoDB and Spring Data Redis on Spring Boot 4.1.1: @Document, String vs ObjectId ids, the _class field, embedded vs @DocumentReference with the queries each sends, MongoRepository and MongoTemplate with the logged commands, $push/$inc vs load-modify-save under 50 threads, @Version, whether Boot creates @Indexed indexes, COLLSCAN vs IXSCAN on 300,000 documents, an aggregation pipeline, transactions on a replica set, a renamed field, RedisTemplate serialization, INCR, sorted sets, hashes, TTL, @RedisHash keys and phantom keys, pipelining and Lettuce.
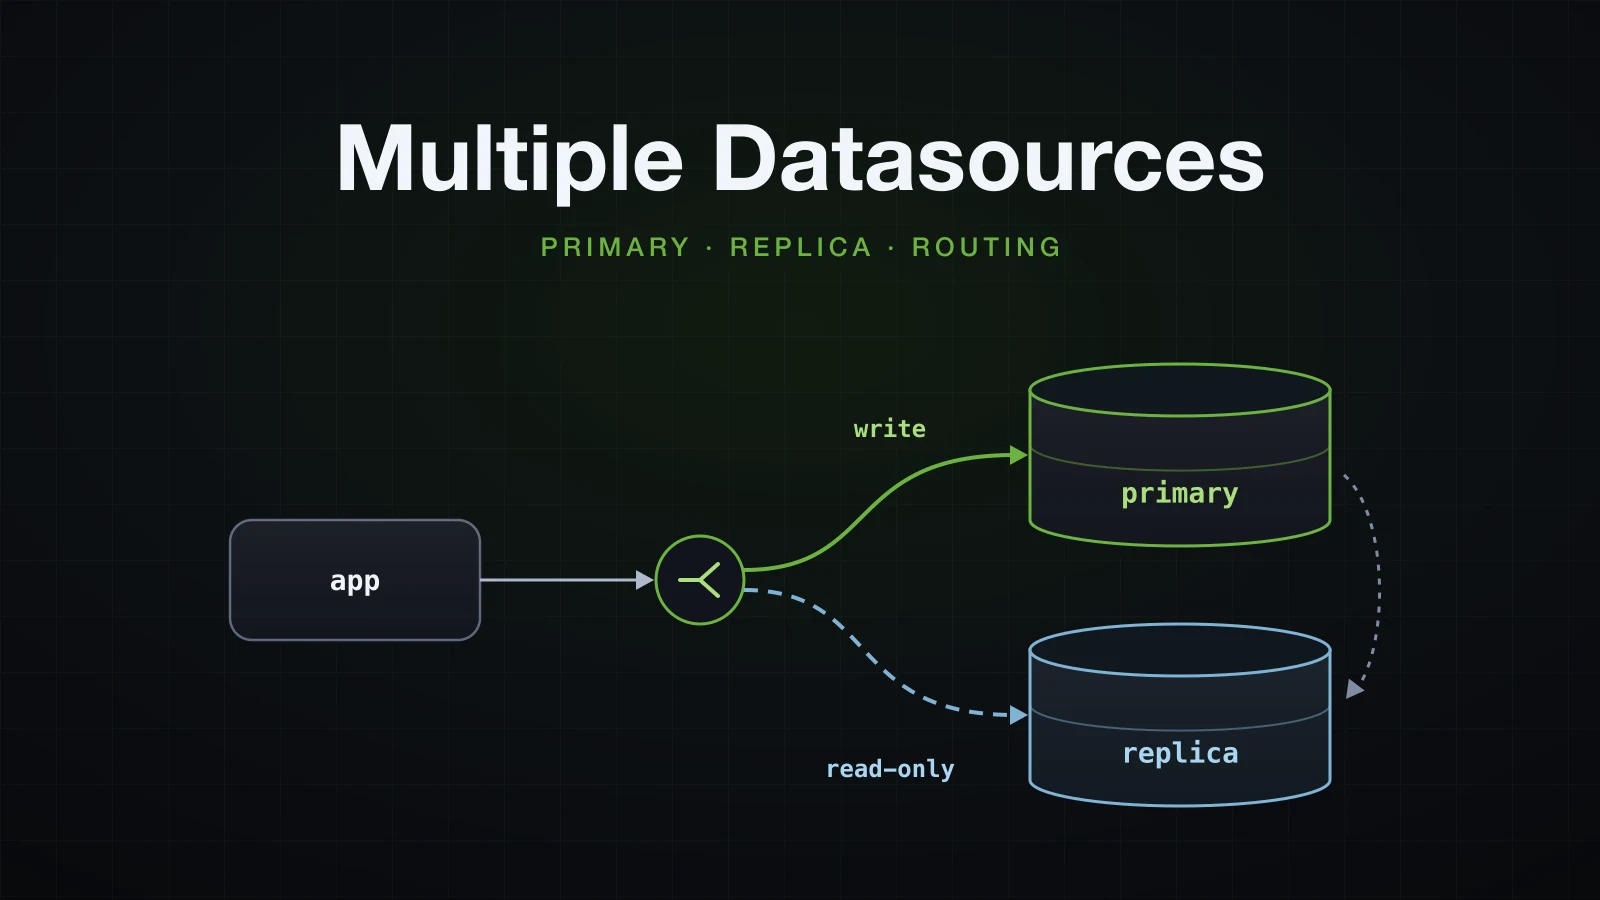
[Advanced Spring Boot] Multiple Datasources in Spring Boot: Two Databases and Read/Write Replica Routing
Multiple datasources in Spring Boot 4.1.1 with PostgreSQL: what Boot backs off from once you declare two DataSource beans, DataSourceProperties and the HikariCP prefix trap, two EntityManagerFactories with EntityManagerFactoryBuilder, @EnableJpaRepositories and @Transactional(transactionManager), a repository under the wrong transaction manager, Flyway for the second database, why a write to two databases is not atomic, a streaming replica in Docker, AbstractRoutingDataSource and the read-only flag bug, LazyConnectionDataSourceProxy and its built-in read-only DataSource, SQLSTATE 25006, replication lag and read-your-writes fixes, and one HikariCP pool per target.
[Advanced Spring Boot] Caching in Spring Boot: the Cache Abstraction, Caffeine, Redis and Invalidation
Spring Boot 4.1.1 caching on a product lookup with PostgreSQL and Redis: why @EnableCaching is still required, @Cacheable, @CachePut, @CacheEvict with allEntries and @Caching, SimpleKey and SpEL keys, condition, unless and cached Optional nulls, the LazyInitializationException a cached entity causes, Caffeine eviction and the cache.gets metrics, why Boot picks Redis over Caffeine, JDK serialization versus GenericJacksonJsonRedisSerializer for Jackson 3 and the type validator that rejects BigDecimal, the two serializer configurations that silently drop settings, latency with no cache, Caffeine and Redis, a cache stampede that sync = true does not stop on Redis, the evict-before-commit race and transactionAware(), stale reads across two instances, and what a stopped or hung Redis does to requests with and without a CacheErrorHandler.